On 19 November 2026, PHP publishes fixes for 17 security advisories, seven of them critical. These critical PHP fixes concern the engine that runs websites, with exposure varying according to their configuration. We advise deploying the update for each branch in use, and checking that the site actually works after the intervention.
Critical PHP patches: which versions should you install?
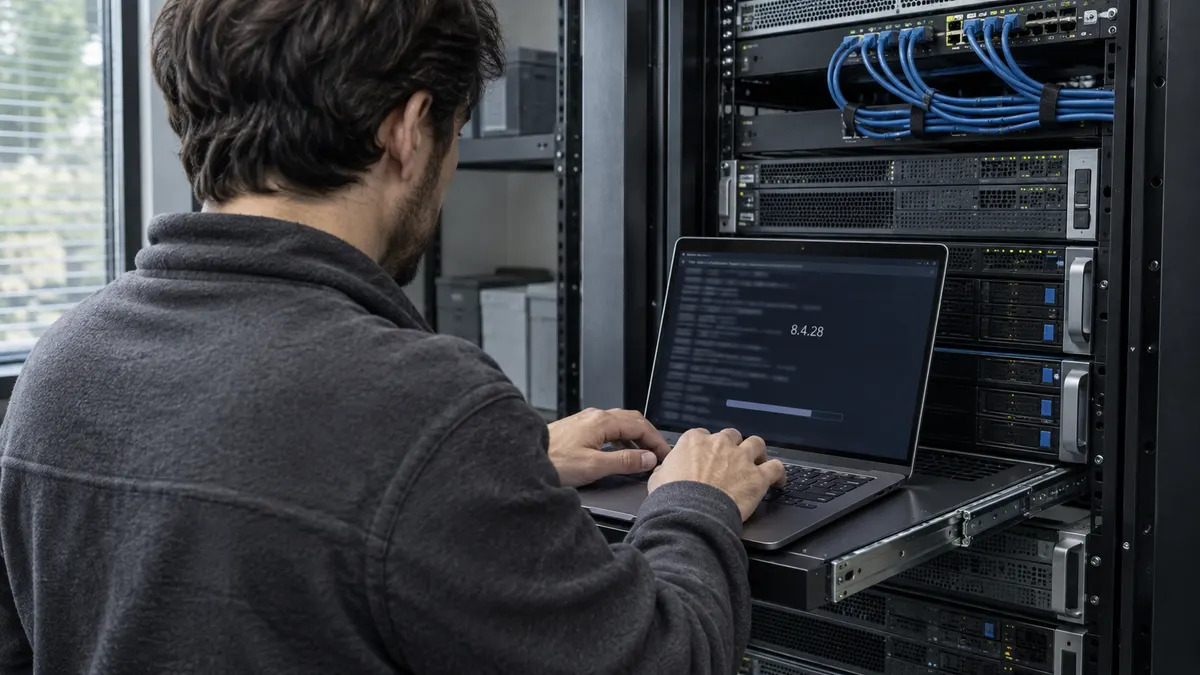
The fixed versions are 8.2.36, 8.3.37, 8.4.28 and 8.5.13. PHP 8.6.0 also contains the fixes. For a site running PHP 8.4, the target is therefore 8.4.28: moving to a new branch is not a prerequisite for the fix.
According to Cloudflare, the batch includes seven critical advisories, four high and six medium. The seven critical ones receive a severity score of 9.2 out of 10. This rating describes the possible consequences, without meaning that every installation allows an attack.
The fixes notably concern sessions, memory and error traces. A session keeps information between several visits or actions by a user. The announcement follows on from our news item on the PHP fixes of 19 November: the versions are now available for deployment.
Which servers meet the conditions for an attack?
Take a shop whose web server passes requests to PHP-FPM, the service that runs PHP. A flaw makes it possible to slip a hidden request into the data of another request. It can lead to code being executed with the rights of that service.
Two conditions combine: the server reuses its FastCGI connections to PHP, and the application opens the data it receives without reading it entirely. FastCGI here refers to the communication protocol between the two components. The nginx setting fastcgi_keep_conn enabled therefore does not prove, on its own, that the shop is usable.
The demonstrated scenario also requires knowing the path of an existing PHP script. Conversely, closing the FastCGI connection after each request blocks this attack. This distinction helps the team rank the servers to handle first.
Another flaw, phpAfterShell, concerns partially rewritten session files. Code execution requires additional conditions, including an interruption at the right moment and an exploitable sequence in the application. As of 19 November, Cloudflare reports no confirmed exploitation of the 17 flaws in the wild.
How do you organise the intervention on a shop?
For the shop, prepare an intervention with a named person in charge and a validation slot. Ask for a usable backup and a rollback procedure before any change. Specify who decides on the rollback if orders stop going through.
Separate installing the fix from business validation. The technical check covers the version actually loaded; the business check covers customer actions. An accessible home page does not, on its own, validate the purchase journey.
So plan a test account, a basket and a control order suited to your environment. Add the automatic payment notifications, called webhooks, and the exchanges with your management tools. Note the expected result for each step before you start.
A web application firewall, often called a WAF, filters some malicious requests but does not fix PHP. Keep this protection as a complement to the deployment.
What evidence should you ask for to close the update?
-
Which version actually answers visitors? Record it for each site and each PHP-FPM process group. Do not limit yourself to the version shown in the terminal. For a package patched by the distribution, require the reference of its security advisory.
-
Which settings are still active? Have them recorded
session.upload_progress.enabled,session.serialize_handlerandsession.save_handler: they govern shipment tracking, the format and the storage of sessions. Add FastCGI reuse to this checklist. -
Is the change in effect and tested? Include rebuilding the container images if necessary, then restarting PHP-FPM or Apache. Then record the results for login, ordering, payment and API, the interfaces used by your other software.